Product · AI-Augmented EASM
Attack Surface Management
Continuous vulnerability management and AI pentesting of your network perimeter, delivered as part of our External Attack Surface Management platform.
- Continuous asset discovery
- Perimeter AI pentesting
- Always-on monitoring
SignalRed EASM
Continuous insight into your external security posture
Discovery, monitoring and testing of everything you expose to the internet, with analysts and AI agents behind the platform.
External attack surface management
A single platform that runs numerous vulnerability scanners and open-source intelligence tools continuously against your network perimeter.
AI pentesting of the perimeter
Beyond the self-service platform, our support team supervises the process, develops custom vulnerability templates and triages findings, with AI pentest agents testing what the scanners expose.
Full-stack outsourcing
Combined with Secure SDLC and PTaaS, this becomes a full external security department at your service.
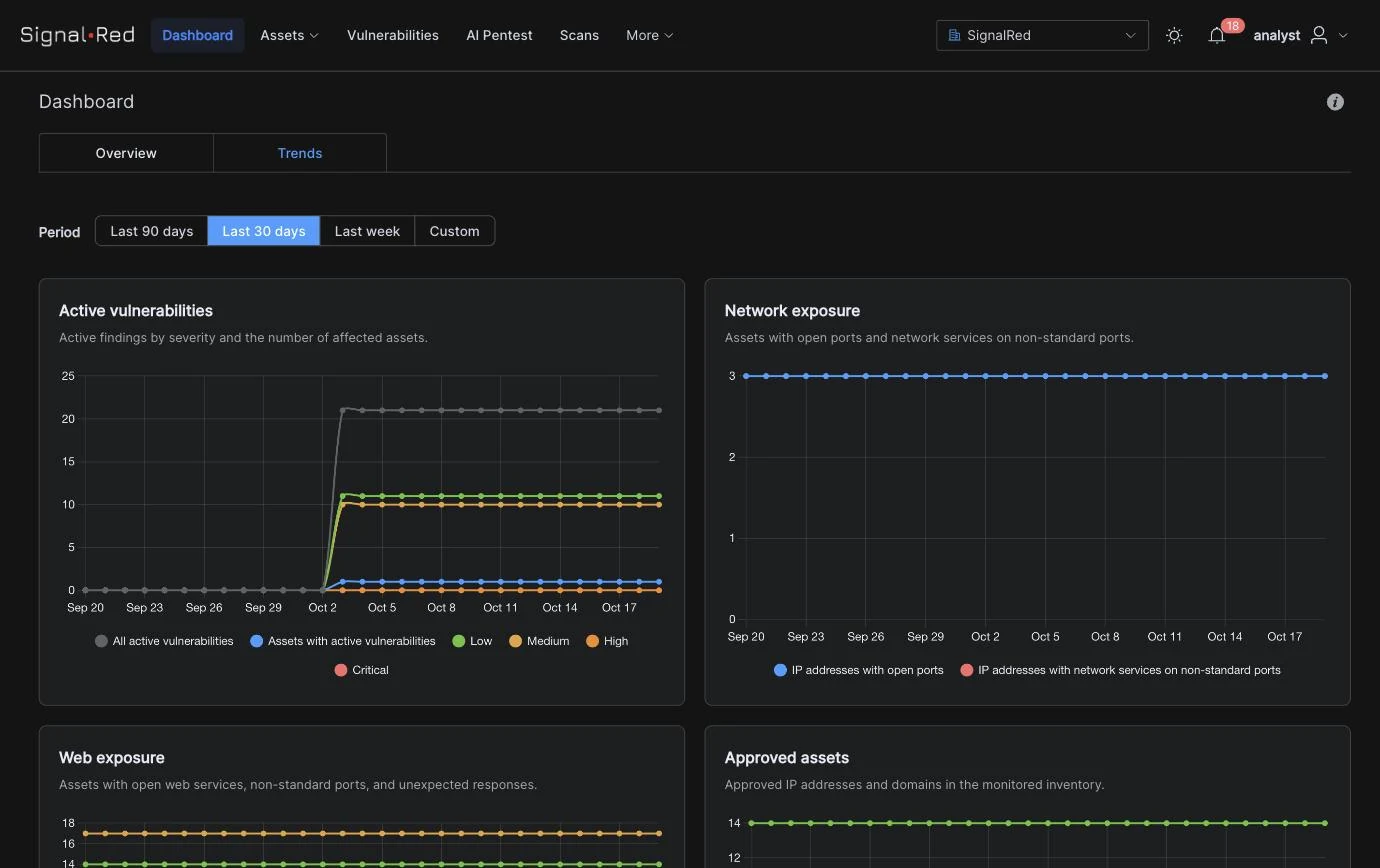
Inside the platform
One view of the perimeter, kept current
Tell us about your footprint and we will tailor the platform and the testing cadence to your business priorities.
Get a quote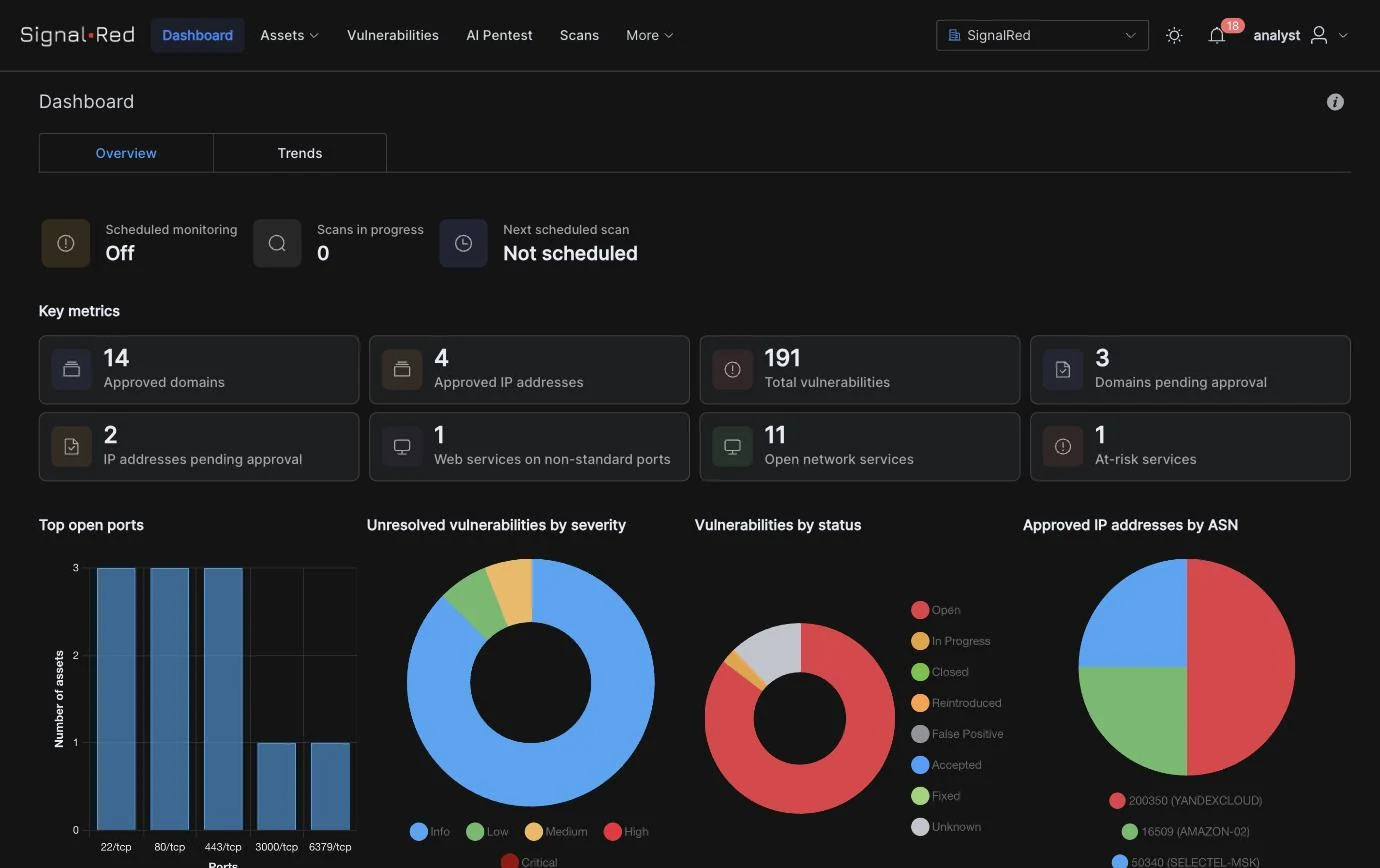
- 30+
- Security engineers on the team
- 50+
- Customers secured every year
- 10+
- Notable awards received in the last three years
Questions
Attack surface management FAQ
What EASM is, what our platform discovers, and how AI pentesting makes it different from a scanner.
What is External Attack Surface Management (EASM)?
External Attack Surface Management is the continuous discovery, inventory, monitoring and testing of every internet-facing asset an organisation owns — domains, subdomains, IP addresses, cloud services, web applications and APIs — to find exposures before attackers do.
What makes SignalRed's EASM 'AI-augmented'?
In addition to classic asset discovery and vulnerability scanning, SignalRed EASM launches AI pentest agents from our Breachloom platform against newly discovered or changed perimeter assets. Findings are confirmed with proof-of-concept evidence and triaged by our analysts, so you get verified vulnerabilities, not scanner noise.
What does the EASM platform discover and monitor?
Domains and subdomains, A/AAAA records and IP ranges, open ports and network services, web services on non-standard ports, technologies and versions, certificates, exposed credentials and misconfigurations. Dashboards show key metrics, vulnerabilities by severity and status, exposure trends over time and assets pending approval.
How is EASM different from a vulnerability scanner?
A vulnerability scanner checks a list of assets you already know. EASM first discovers assets you may not know about (shadow IT, forgotten subdomains, staging environments), continuously tracks changes, and in SignalRed's case adds AI pentesting and human triage on top of scanning.
How is EASM priced?
SignalRed EASM is a subscription priced by the size of your external attack surface, with optional supervision by our analysts who develop custom vulnerability templates and triage findings.
Get a quote
Tell us about your scope
We reply within two hours during business hours with next steps and, where the scope is clear, a price.
About SignalRed
US company with teams in London and Dubai
Customers in the US, UK and UAE. CREST Pathway organisation.
- 1Discovery call, 15 minutes
We understand your scope, deadlines and compliance requirements.
- 2Proposal, same day
Fixed price and duration for the agreed scope, valid for 30 days.
- 3Testing starts within 24 hours
Autonomous testing begins immediately; manual engagements are scheduled with a named team.
- 4Report and re-test
An expert-signed report, then a free re-test once you have remediated.
Prefer email? info@signalred.io
Request a quote
No commitment. Free consultation. We never share your details.
Tell us what to test. We will tell you what it takes.
Share your scope and we will recommend the right engagement: autonomous, AI-augmented manual testing, or continuous coverage.
- Response within 2 hours in business hours
- No commitment required
- Fixed price in every proposal