Solution · DevSecOps
Secure SDLC
We build DevSecOps pipelines and embed best-practice security into your development process with our Application Security Orchestration and Correlation platform.
- SAST / DAST / SCA in CI/CD
- ASOC platform
- End-to-end support
SignalRed SDLC
Application security orchestration, built into your pipeline
Existing tools, a custom approach and our platform combined to raise the quality of your development life cycle.
DevSecOps
Our ASOC platform API integrates vulnerability scanners with the CI/CD pipeline and defect tracking. During implementation we add custom testing scenarios for the highest coverage.
Correlation and orchestration
The platform aggregates SCA, DAST, SAST and other tools and correlates their output into actionable dashboards, so remediation is prioritised and time-to-fix improves.
Secure SDLC
We build the components of your Secure Software Development Life Cycle and support them with continuous advisory and security assessment as a service.
Inside the platform
Scanner output, correlated and prioritised
Tell us about your pipeline and tooling and we will design the integration and the support around it.
Get a quote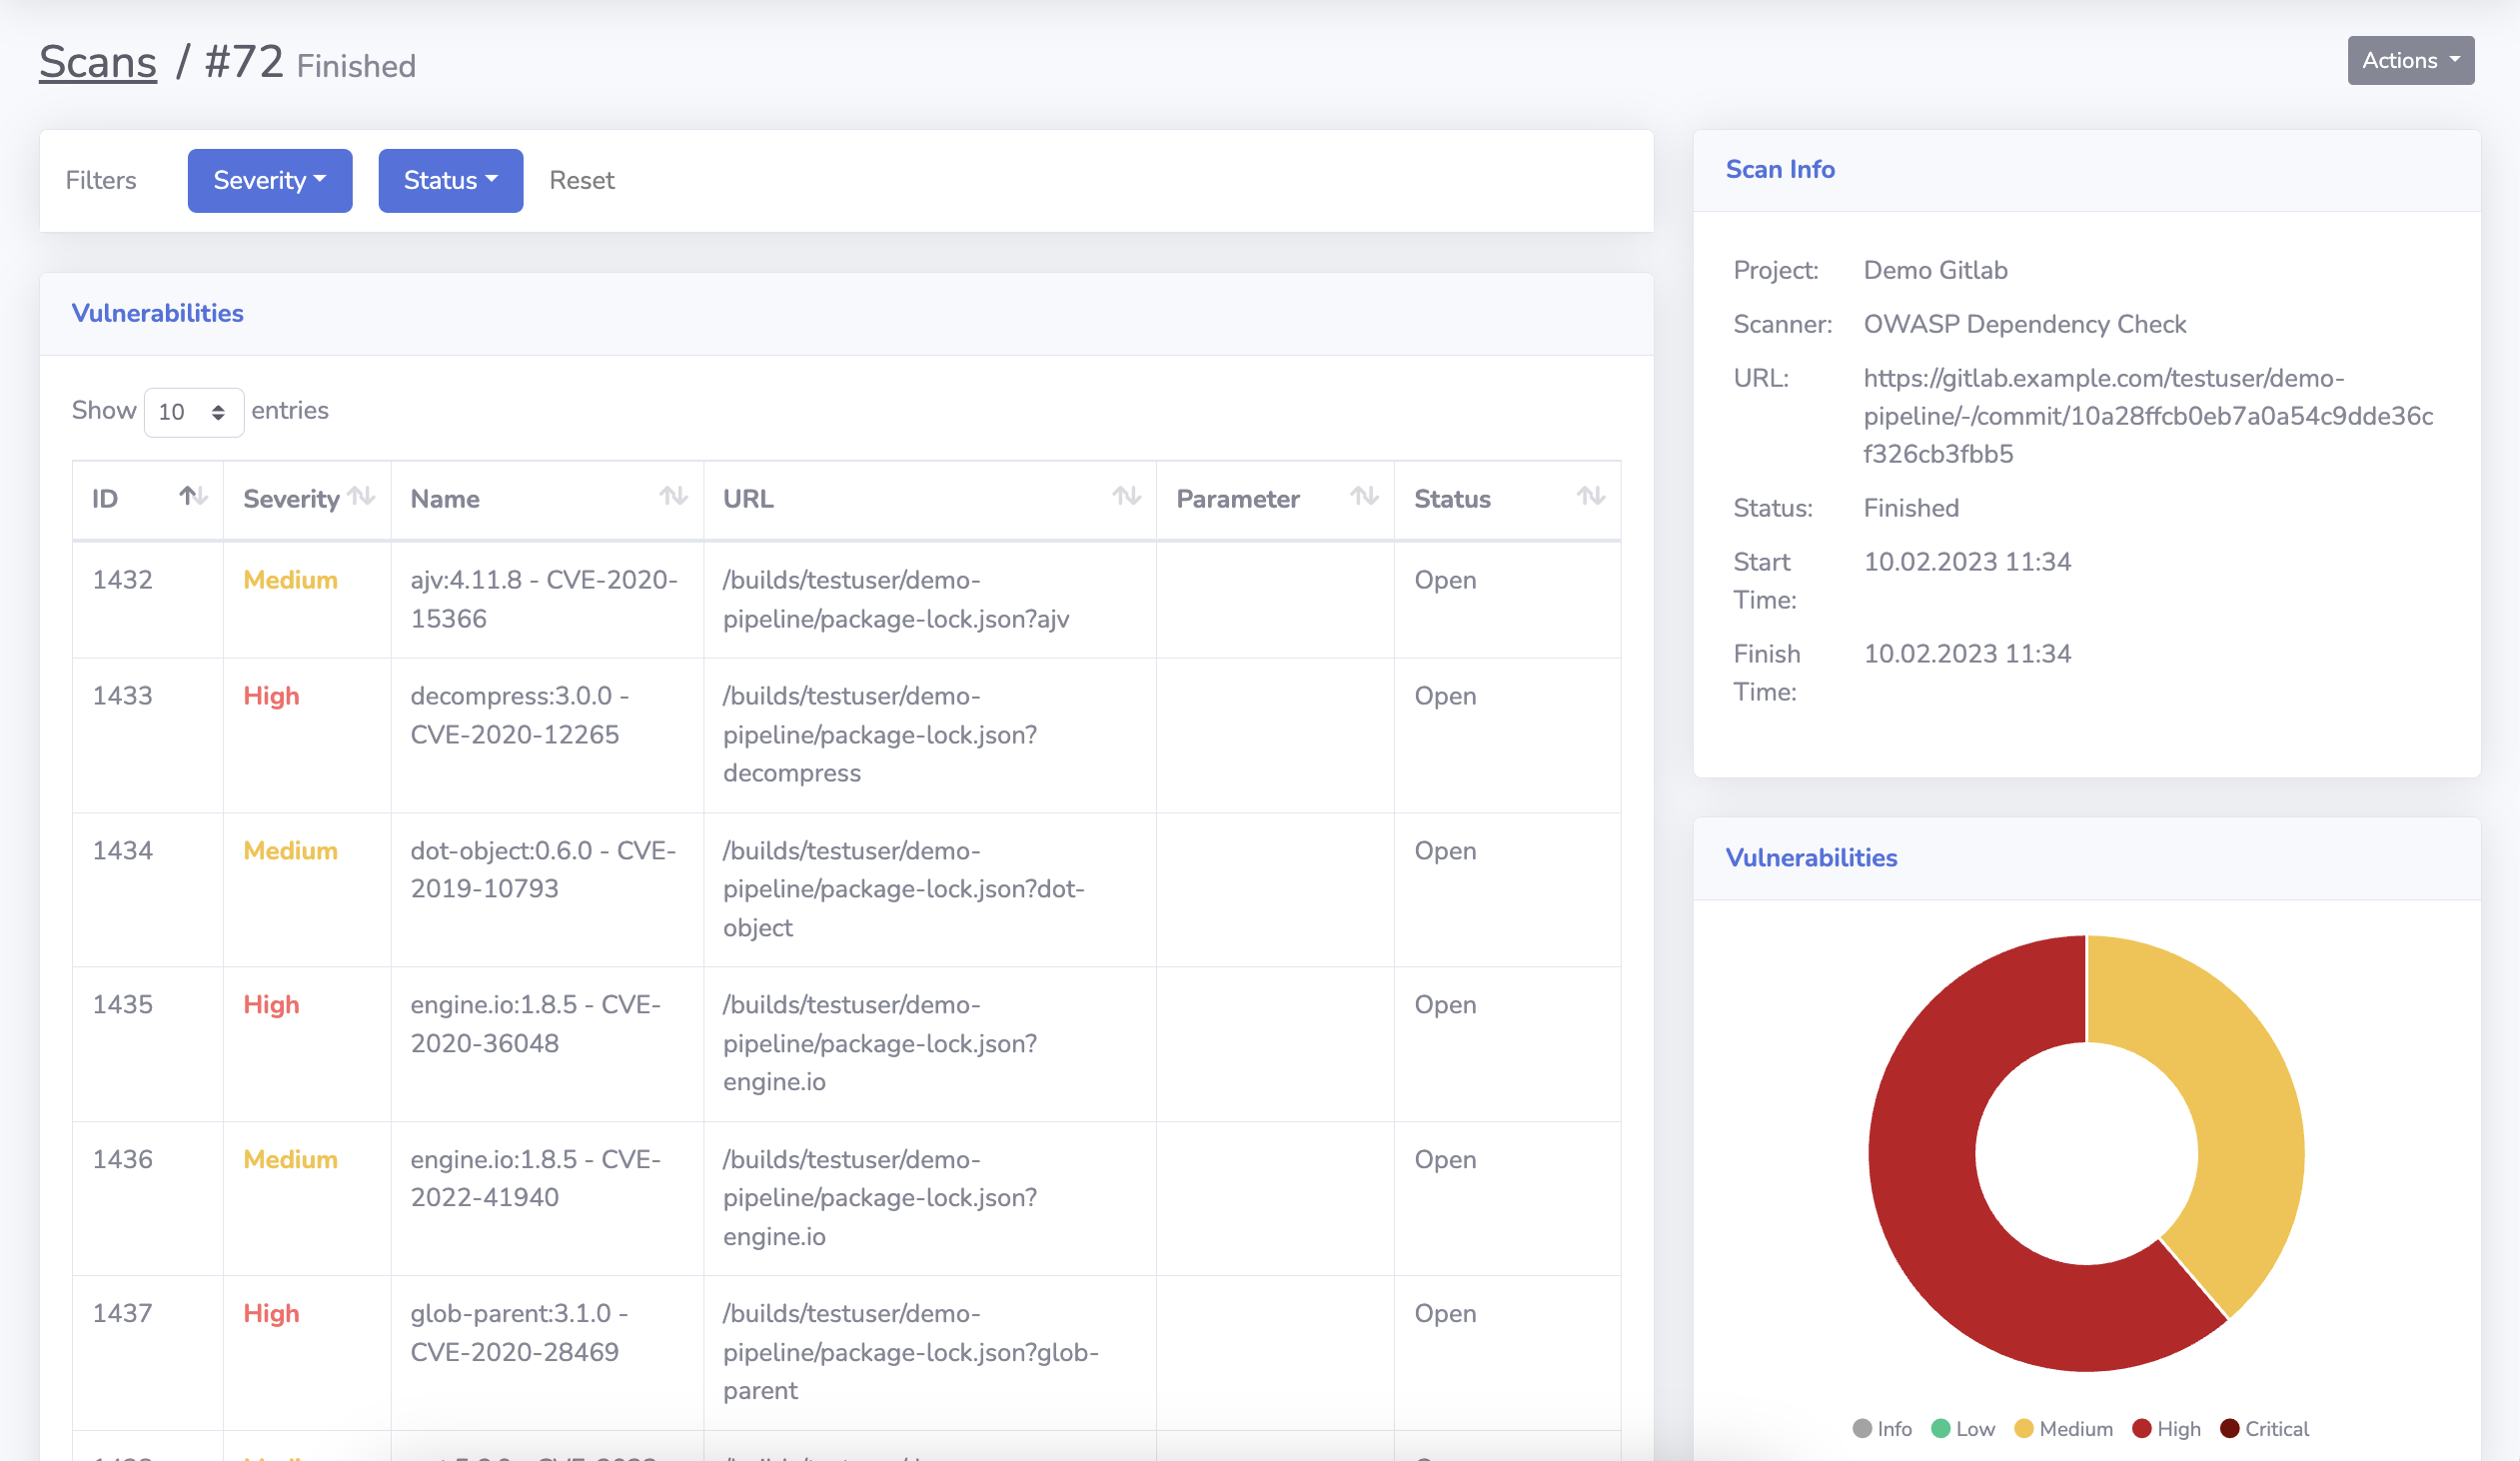
- 30+
- Security engineers on the team
- 50+
- Customers secured every year
- 10+
- Notable awards received in the last three years
Questions
Secure SDLC FAQ
What a Secure SDLC and an ASOC platform are, and how we implement DevSecOps.
What is a Secure SDLC?
A Secure Software Development Life Cycle embeds security activities — threat modelling, secure coding standards, SAST, DAST, SCA, secrets scanning and security testing — into every phase of software development, so vulnerabilities are prevented or caught before release.
What is an ASOC platform?
Application Security Orchestration and Correlation (ASOC) aggregates the output of security scanners (SAST, DAST, SCA, IaC and container scanning), deduplicates and correlates findings, pushes them to defect trackers and produces actionable dashboards that prioritize remediation and improve time-to-fix.
How does SignalRed implement DevSecOps?
We integrate scanners into your CI/CD pipelines through our ASOC platform API, add custom testing scenarios for your stack, connect results to Jira or similar trackers, define security gates and train your developers. Ongoing advisory and security assessment as a service keep the process effective.
Which tools do you integrate?
Both open-source and commercial SAST, DAST, SCA, secrets and container scanners, chosen to match your languages and infrastructure. The ASOC platform is tool-agnostic and correlates results from any source.
Get a quote
Tell us about your scope
We reply within two hours during business hours with next steps and, where the scope is clear, a price.
About SignalRed
US company with teams in London and Dubai
Customers in the US, UK and UAE. CREST Pathway organisation.
- 1Discovery call, 15 minutes
We understand your scope, deadlines and compliance requirements.
- 2Proposal, same day
Fixed price and duration for the agreed scope, valid for 30 days.
- 3Testing starts within 24 hours
Autonomous testing begins immediately; manual engagements are scheduled with a named team.
- 4Report and re-test
An expert-signed report, then a free re-test once you have remediated.
Prefer email? info@signalred.io
Request a quote
No commitment. Free consultation. We never share your details.
Tell us what to test. We will tell you what it takes.
Share your scope and we will recommend the right engagement: autonomous, AI-augmented manual testing, or continuous coverage.
- Response within 2 hours in business hours
- No commitment required
- Fixed price in every proposal