AI-Augmented Service
Application Security Testing
AI-augmented application security testing with a unique methodology that combines industry-leading standards with a business-specific approach.
- Web, mobile & API coverage
- Manual + AI testing
- Zero false positives
How we assess applications
Application security assessment, delivered in an agile way
Web, mobile and API assessments delivered through live dashboards as well as PDF reports.
Coverage
Every endpoint, API method, server-side route and source file. We go through each component of the system and test as many attack scenarios as possible.
Impact
Real vulnerabilities instead of low-risk vanity findings that bloat reports. Critical issues come with an exploitation demonstration and a risk assessment.
Remediation
Detailed remediation guidance, post-engagement consultations and a free round of re-testing to confirm every identified vulnerability is resolved.
How we work
From scope to secure, in four steps
A transparent, predictable engagement, tailored to your industry, technical stack and business priorities.
- 1
Scoping
We define exactly what to test: applications, source code, network hosts, APIs, internal networks, Wi-Fi, SaaS accounts, along with dates and legal requirements.
- Start date and deadline
- IPs, subnets and API endpoints
- Web and mobile applications
- Other in-scope assets
- 2
Proposal
A technical and commercial proposal tailored to your request. Valid for 30 days, it includes one free re-test and 12 months of support.
- Description and scope of work
- Fixed price
- Timeline and duration
- Contract with a legal entity
- 3
Pentest
We follow proven methodologies: OWASP Testing Guide, MASTG, OSSTMM, CBEST, TIBER. The report details every finding with remediation guidance and an executive summary.
- Reconnaissance
- Vulnerability identification
- Exploitation
- Reporting
- 4
Support
For 12 months after the engagement we provide clarifications, a remediation strategy and one free re-test of all issues with an updated final report.
- Remediation strategy
- Expert consulting
- Free re-testing
What you receive
Findings you can hand straight to the development team
Tell us about the application, its stack and the access you can provide, and we will propose the scope and the price.
Get a quote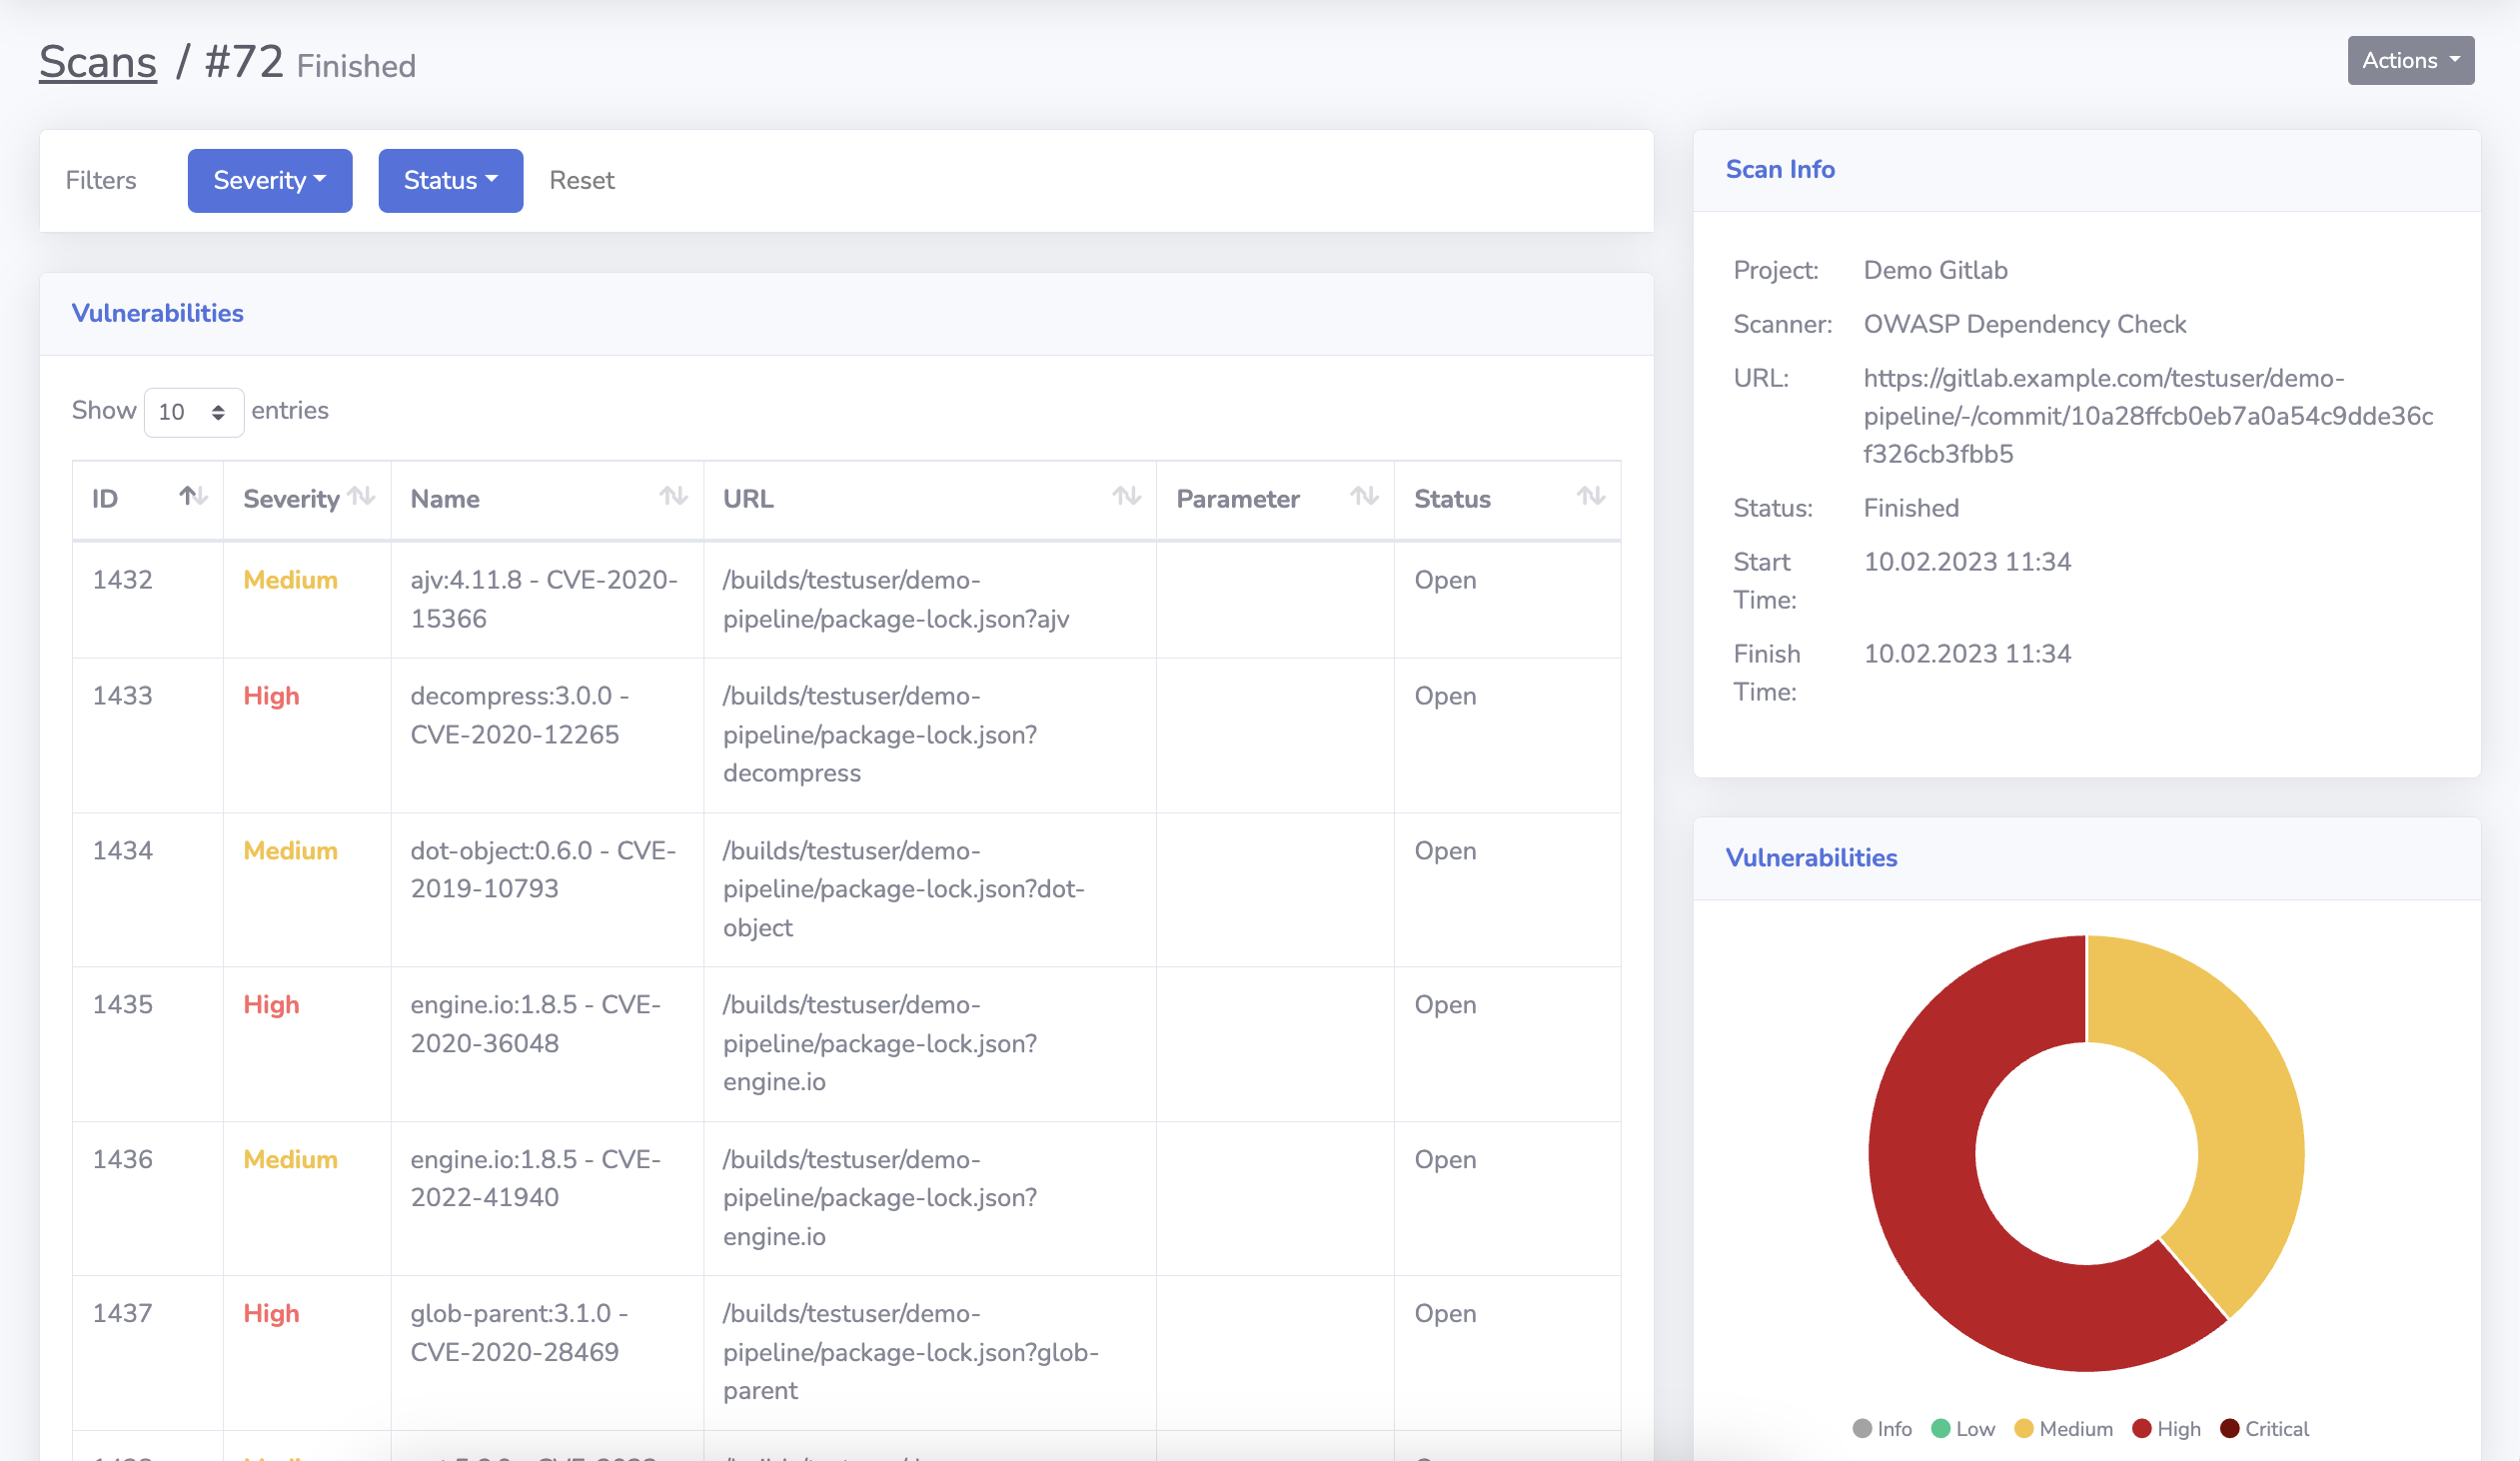
- 30+
- Certified penetration testers on the team
- 50+
- Customers secured every year
- 10+
- CTF competition wins in the last three years
Accredited and certified
CREST Pathway organisation. Testers hold OSCP, OSEP, OSWE, BSCP and further offensive certifications.
Questions
Application security testing FAQ
Coverage, standards, business-logic testing and deliverables.
What does application security testing cover?
SignalRed's application security testing covers web applications, mobile applications (iOS and Android), REST and GraphQL APIs and the source code behind them. We test every endpoint, API method and route for injection, authentication and authorization flaws, business-logic abuse, cryptographic weaknesses, client-side issues and financial-logic errors.
Which standards does the assessment follow?
Assessments follow the OWASP Web Security Testing Guide, OWASP API Security Top 10, OWASP ASVS and OWASP MASTG, combined with SAST and DAST tooling whose output is manually verified to eliminate false positives.
Do you test business logic and payment flows?
Yes. Business and financial logic is a core focus: double spending, rounding errors, transaction amount tampering, race conditions, mass assignment, IDOR and privilege escalation. Many of our customers are fintech companies, banks and payment gateways that need this depth for PCI DSS and regulatory requirements.
What do we receive at the end?
You receive a PDF report with an executive summary, a description of the inventory and data flows, every finding with risk level, exploitation steps and remediation advice, plus access to our PTaaS dashboard. One free re-test confirms that fixes are effective and the final report reflects remediation status.
How is this different from the Autonomous AI Pentest?
The Autonomous AI Pentest (from $3,000) is run by AI agents with expert validation and is ideal for fast, compliance-driven coverage. The application security assessment is a manual, AI-augmented engagement led by senior testers and is recommended for complex applications, fintech logic and source-code review.
Get a quote
Tell us about your scope
We reply within two hours during business hours with next steps and, where the scope is clear, a price.
About SignalRed
US company with teams in London and Dubai
Customers in the US, UK and UAE. CREST Pathway organisation.
- 1Discovery call, 15 minutes
We understand your scope, deadlines and compliance requirements.
- 2Proposal, same day
Fixed price and duration for the agreed scope, valid for 30 days.
- 3Testing starts within 24 hours
Autonomous testing begins immediately; manual engagements are scheduled with a named team.
- 4Report and re-test
An expert-signed report, then a free re-test once you have remediated.
Prefer email? info@signalred.io
Request a quote
No commitment. Free consultation. We never share your details.