Get an expert-validated AI pentest done. This week.
Start your network, web application or API pentest today on Breachloom, our AI pentest platform. A certified human expert verifies every finding and signs off the PDF report, delivered in one business day and ready for SOC 2, ISO 27001, PCI DSS and HIPAA audits.
Tell us what to test. We reply within two hours during business hours.
About SignalRed:US company with teams in London and Dubai
Human expert sign-off on every finding · Compliance-ready for SOC 2, ISO 27001, PCI DSS, HIPAA · GDPR compliant
Why autonomous
The speed of AI, the judgement of a senior tester
Breachloom runs hundreds of specialised agents in parallel. Certified experts supervise the run, validate every finding and sign the report.
Verified by human experts
The AI does the testing; a certified security expert reviews every finding, verifies exploitability and signs off on the final report. Nothing reaches you unchecked.
Infrastructure and application testing
Infrastructure vulnerabilities and application security flaws covered in a single engagement.
One business day
Testing starts immediately after scoping and the complete report arrives in one business day, not weeks.
Compliance-ready
Audit-grade reports that meet the penetration testing requirements of SOC 2, ISO 27001, PCI DSS, HIPAA, DORA, NIS2 and every other framework your auditors expect.
Zero false positives
Every vulnerability is reproduced with a proof-of-concept exploit. Only confirmed findings make it into the report.
Detailed remediation
Evidence, reproduction steps, risk ratings and concrete remediation guidance for each finding.
Need a pentest report before your audit?
Testing starts within 24 hours of scoping. A certified expert verifies every finding and signs the report, which arrives one business day after testing completes and meets the pentest requirements of every major framework.
Autonomous agents map the attack surface: applications, APIs, infrastructure components and every potential entry point.
2
Exploitation
Hundreds of specialised AI agents test each target in parallel, going deep on both infrastructure and application vulnerabilities.
3
Validation
Every finding is reproduced with a proof-of-concept exploit. Only confirmed vulnerabilities proceed to expert review.
4
Expert review
Certified security experts verify exploitability, assess business impact and sign off on the compliance-ready report.
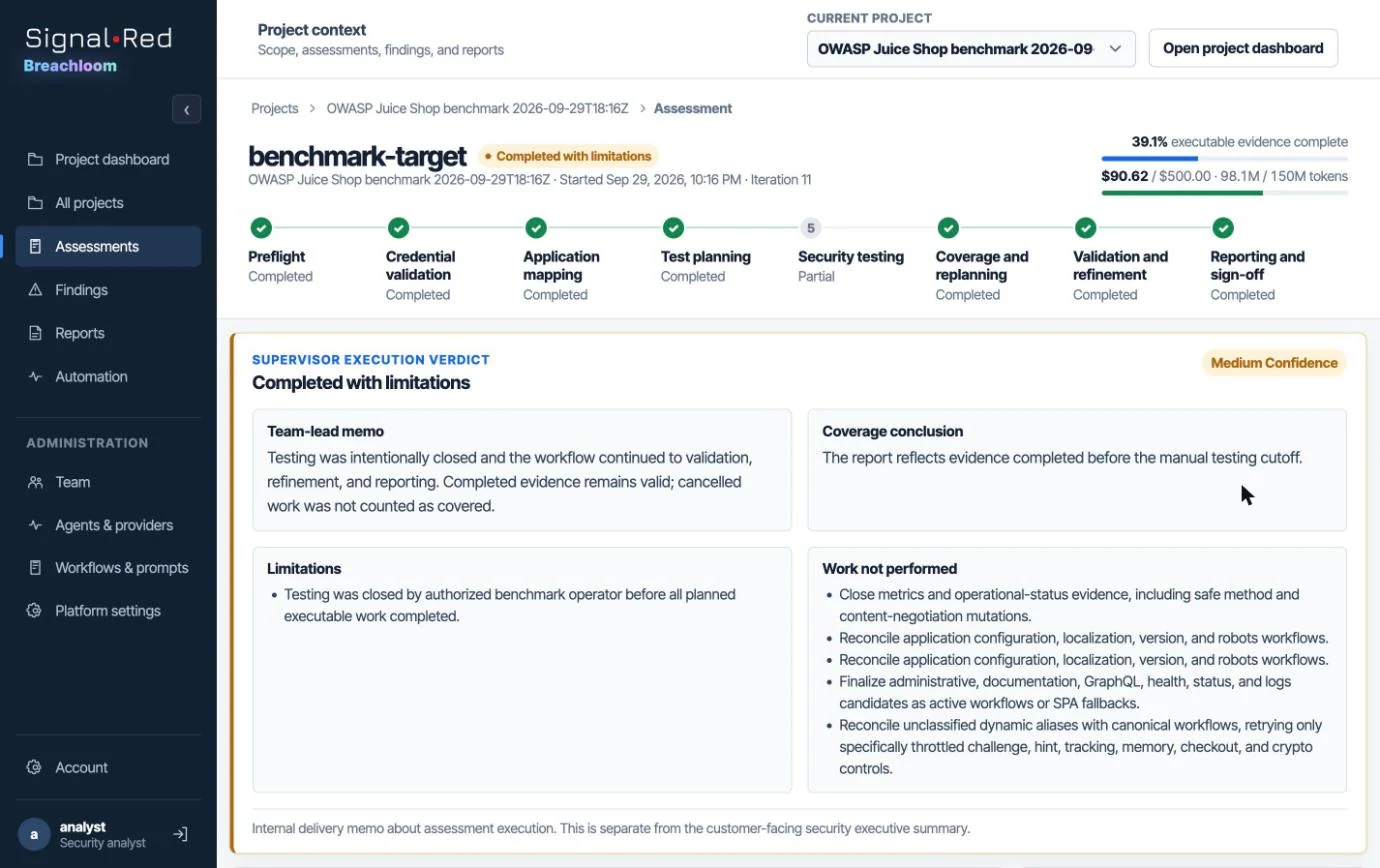
Live assessment pipeline
Every stage is visible in real time, from preflight and credential validation to coverage reconciliation and sign-off.
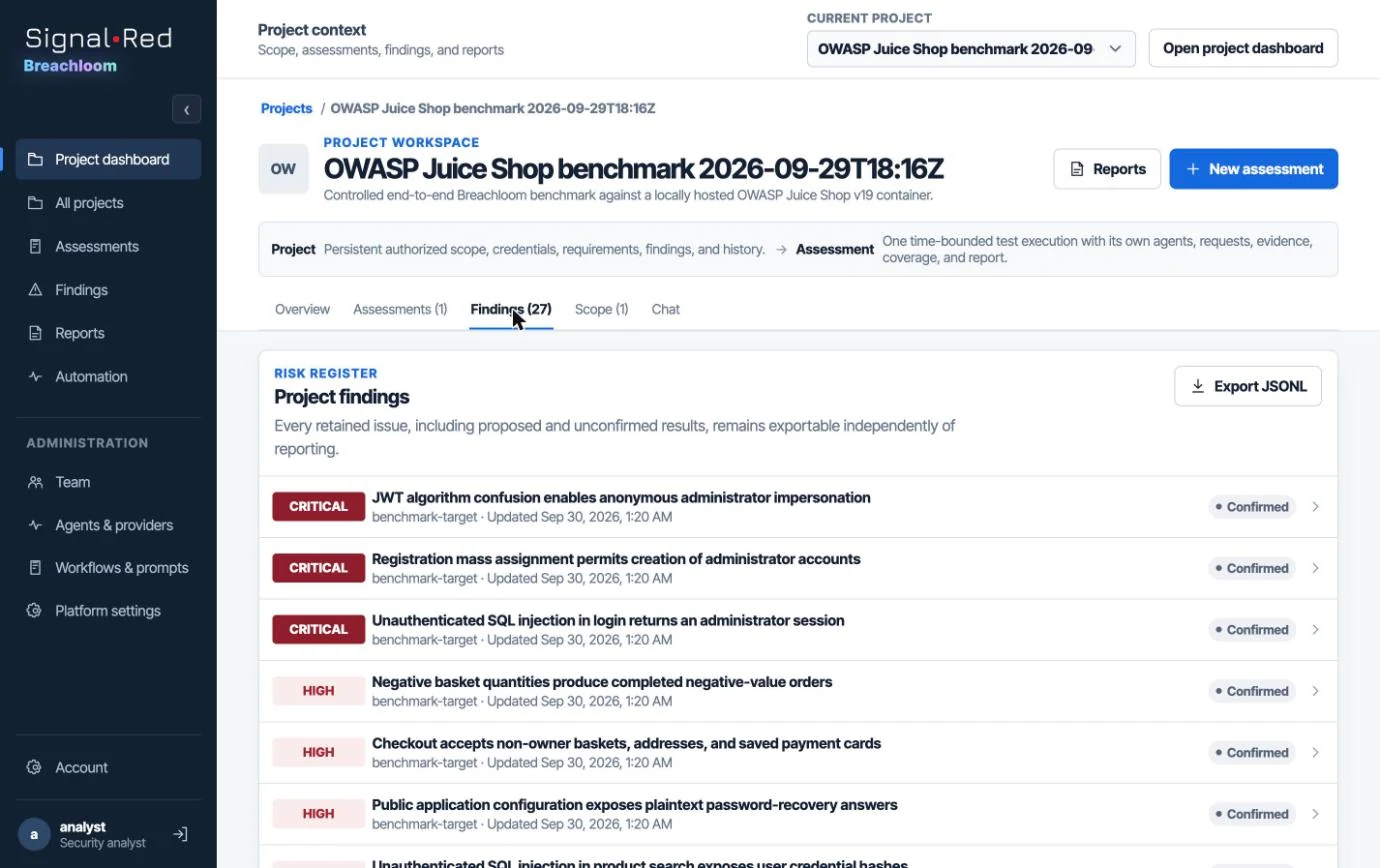
Findings register
Every validated finding, prioritised by severity and ready to remediate.
Inside Breachloom
The autonomous pentest platform, end to end
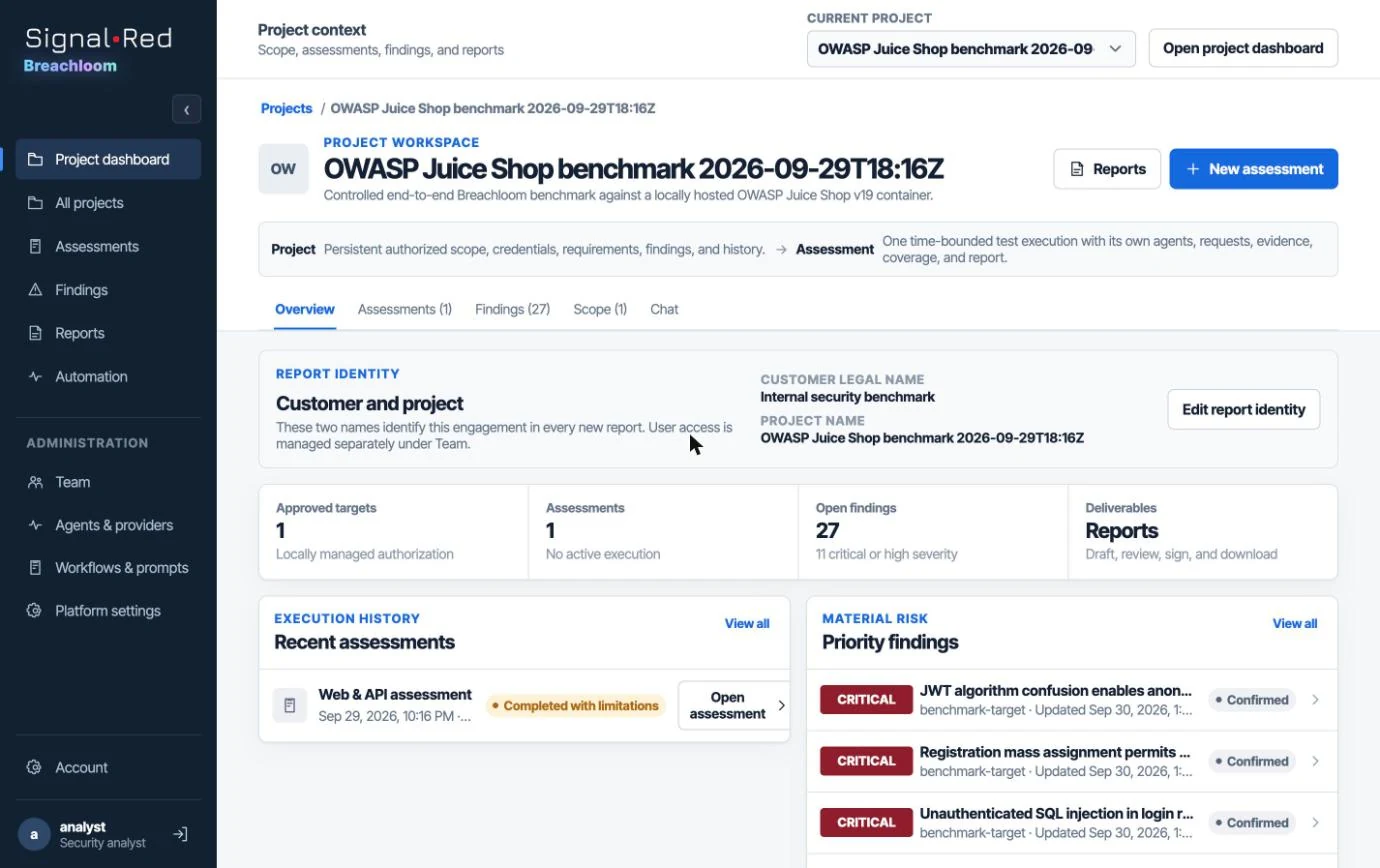
Breachloom is SignalRed's autonomous AI penetration testing platform. The screenshots below are from a real assessment of OWASP Juice Shop, a deliberately vulnerable benchmark application.
Project workspace
One workspace per customer: authorised scope, credentials, assessments, findings and reports, with every action attributable.
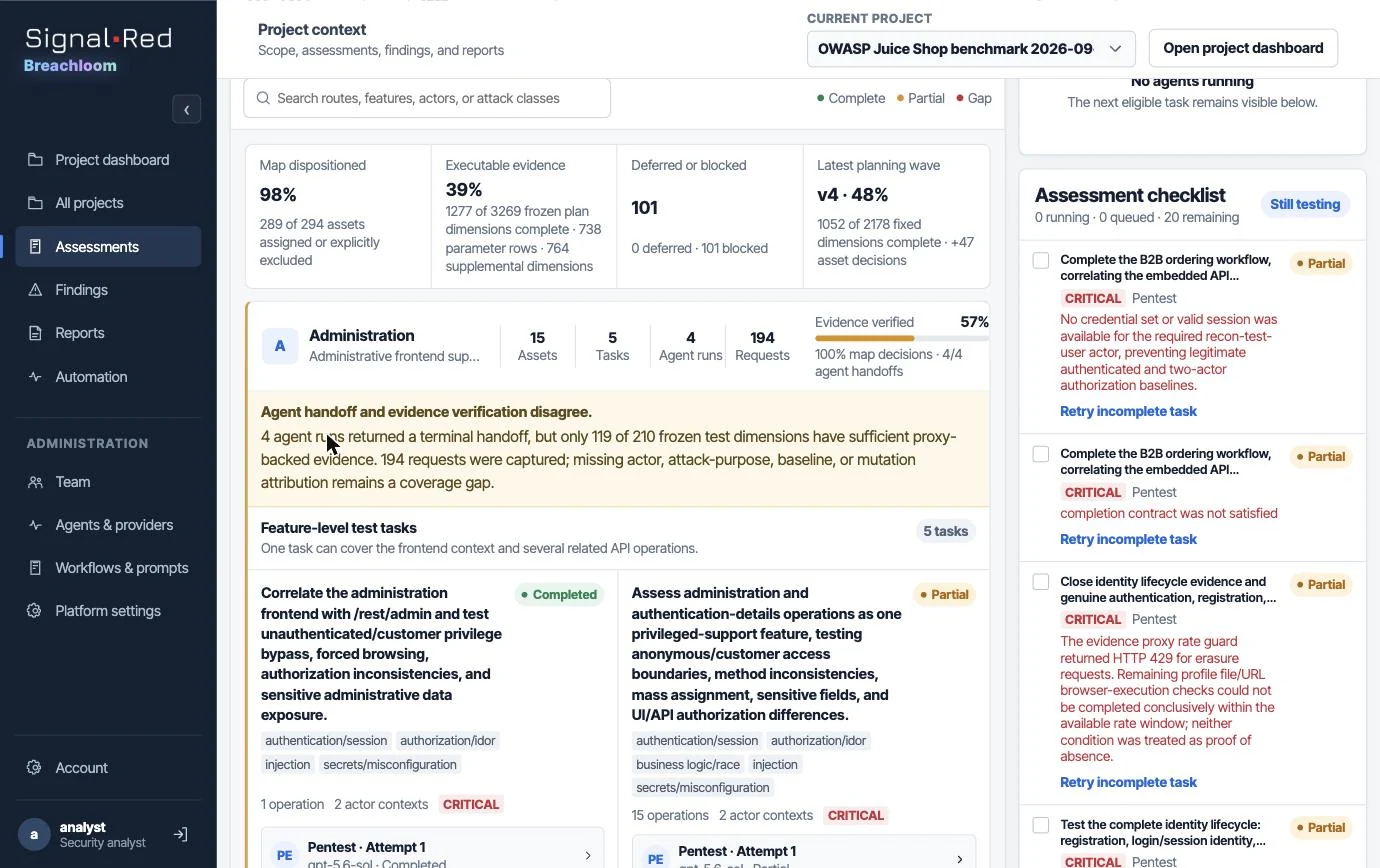
Transparent pipeline
Preflight, credential validation, application mapping, test planning, testing, coverage reconciliation, validation and sign-off. Budget and token usage are visible at every step.
Evidence-backed coverage
Coverage is derived from captured HTTP evidence, not from what an agent claims. Gaps, blocked and deferred work are reported, never silently dropped.
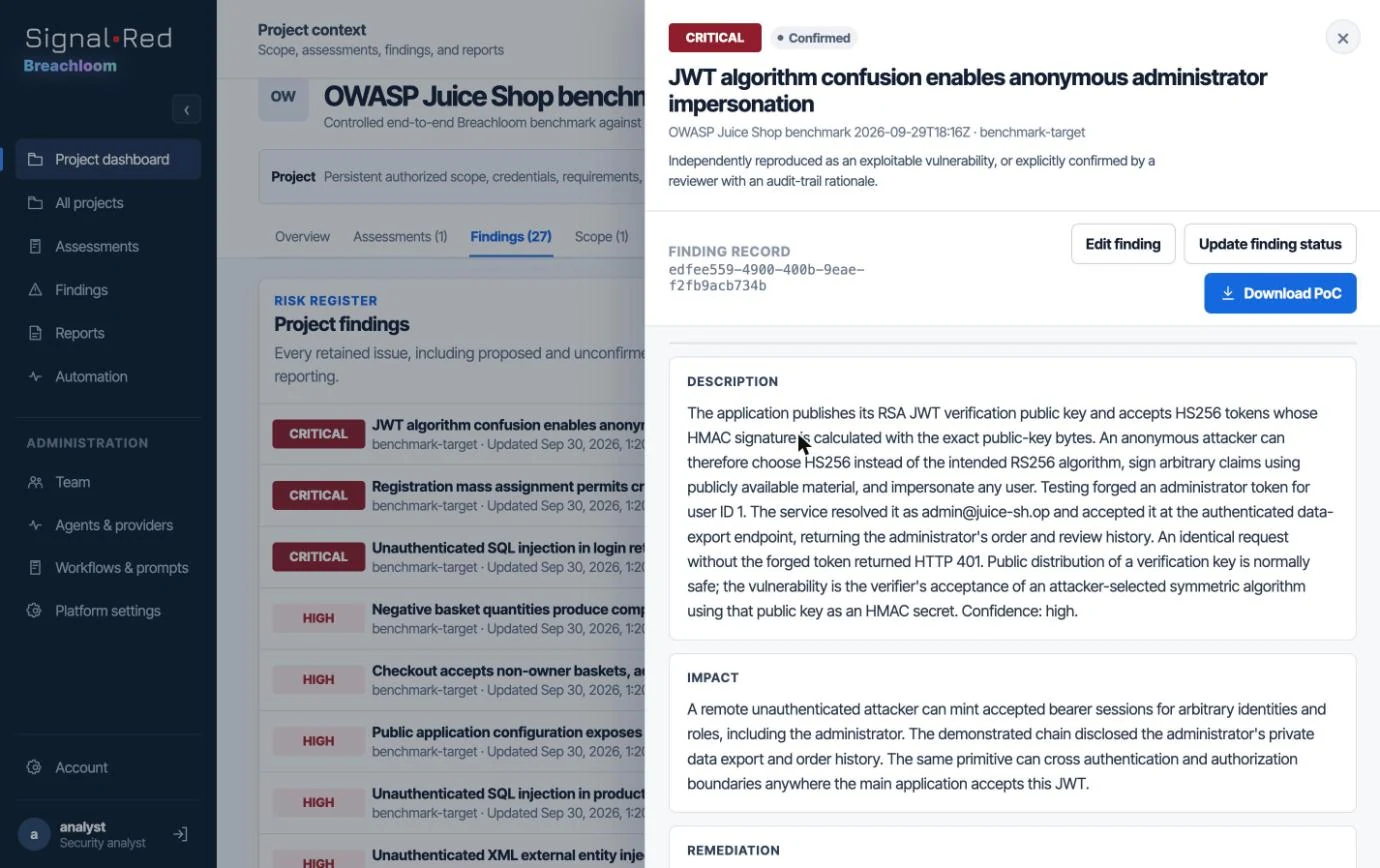
Confirmed findings only
Every finding is independently reproduced before it reaches the report: JWT algorithm confusion, mass assignment, SQL injection, business-logic abuse and more.
Proof, impact, fix
Each finding ships with a reproducible proof-of-concept, business impact analysis and concrete remediation guidance.
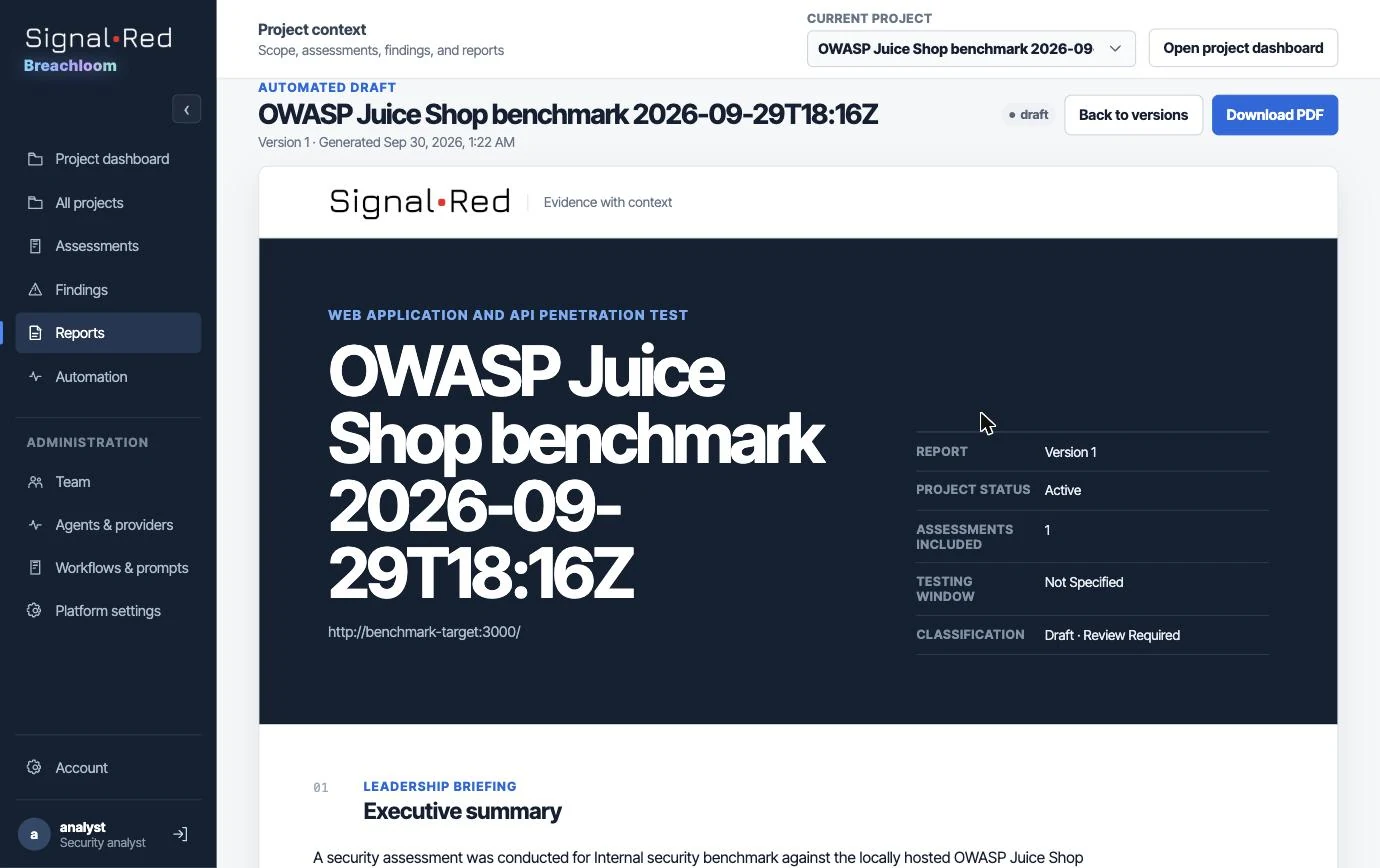
Audit-ready report
Draft reports are generated automatically; the final report is reviewed, versioned and signed by a human expert, ready for SOC 2 or ISO 27001 auditors.
Track record
Built and supervised by a team that competes
The experts who validate every Breachloom finding are the same senior testers who run our manual engagements.
30+
Certified penetration testers on the team
50+
Customers secured every year
10+
CTF competition wins in the last three years
Accredited and certified
CREST Pathway organisation. Testers hold OSCP, OSEP, OSWE, BSCP and further offensive certifications.
Pricing
Simple, transparent pricing
Pricing starts at $3,000, the minimum for a simple website, and scales with scope. Every plan includes human expert validation and a free re-test window. No hidden fees.
Standard
$3,000
from, per test
The minimum, for a simple website or a small infrastructure scope.
Need something between plans or a continuous programme? Contact us for a tailored quote. Manual AI-augmented pentests and red teaming are priced separately.
Compliance
Compatible with every major compliance framework
Executive summary, verified findings with proof-of-concept exploits, risk assessment and remediation guidance, signed off by a certified expert and structured to meet the penetration testing requirements of every framework listed here.
SOC 2
ISO 27001
ISO 27017
ISO 27018
ISO 27701
ISO 42001
HIPAA
GDPR
NIST CSF 2.0
NIST 800-53
NIST 800-171
NIST AI RMF
CMMC
PCI DSS
FedRAMP
CIS Controls
OWASP ASVS
OWASP Top 10
Questions
Autonomous pentest FAQ
What an autonomous AI penetration test is, what Breachloom does, what it costs and how the report holds up with auditors.
What is an autonomous AI penetration test?
An autonomous AI penetration test is a full penetration test in which AI agents perform reconnaissance, planning, exploitation and validation without a human operator driving each step, while certified security experts review and sign off the final report. SignalRed's autonomous pentest runs on our Breachloom platform and delivers an expert-validated, compliance-ready report in 1 business day.
What is Breachloom?
Breachloom is SignalRed's autonomous AI penetration testing platform. It validates the authorized scope and credentials, maps the application, builds a risk-prioritized test plan from OWASP WSTG, OWASP Top 10 and OWASP API Top 10, runs hundreds of specialised agents in parallel, records every request through a scope-enforcing evidence proxy, reconciles coverage against captured evidence rather than agent claims, independently reproduces findings, and generates a draft report that a human expert reviews and signs.
What does the autonomous pentest cover?
The Standard plan covers external infrastructure and unauthenticated web application testing with OWASP Top 10 coverage. The Advanced plan adds authenticated web application testing with multiple user roles, REST and GraphQL API security testing, business-logic testing and extended infrastructure coverage. Enterprise scopes can include custom targets, continuous testing and dedicated experts.
How is it different from a vulnerability scanner?
A scanner matches signatures and reports suspected issues, many of them false positives. Breachloom behaves like a penetration tester: it understands the application's features and roles, chains weaknesses into real attack paths, proves exploitability with a working proof-of-concept, and tracks what was and was not tested in an evidence-backed coverage matrix. Only confirmed, reproduced vulnerabilities reach the report.
Are findings validated by humans?
Yes. Every finding is first reproduced by an independent validation agent and then reviewed by a certified SignalRed penetration tester who verifies exploitability, assesses business impact and signs off the final report. Automated drafts and approved reports are clearly distinguished.
How fast can we start and when do we get the report?
Testing can start within 24 hours of scoping and authorization, and the expert-validated PDF report is delivered in 1 business day. Our team responds to requests within 2 hours during business hours.
How much does the autonomous pentest cost?
Pricing starts at $3,000, which is the minimum for a simple website (Standard plan). The Advanced plan starts at $5,000 and the Enterprise plan is quoted individually. There are no hidden fees; the price is agreed up front based on scope.
Is the report suitable for SOC 2, ISO 27001 and customer due diligence?
Yes. Reports include an executive summary, scope and methodology, coverage and limitations, detailed findings with proof-of-concept evidence, risk ratings, remediation guidance and expert sign-off, and are structured for SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NIST CSF 2.0 and other frameworks.
Is it safe to run against production systems?
Yes, with controls. Testing is limited to approved targets only, traffic passes through a scope-enforcing proxy with rate and concurrency limits, destructive techniques are disabled unless you explicitly allow them, you can define constraints and known non-issues, and any accounts, files or records created during testing are cleaned up or reported.
What do we need to provide?
Only the target URLs or IP ranges and written authorization to test them. Optionally you can provide test accounts for each user role, API specifications, source code and documentation, and any testing constraints — the more context you share, the deeper the coverage.
Get a quote
Tell us about your scope
We reply within two hours during business hours with next steps and, where the scope is clear, a price.